Update, October 2026: w3af, which has had no release since 2015, has been removed from this list; ZAP and Burp Suite cover the same ground. ZAP left OWASP in 2023 and is now an independent project supported by Checkmarx (ZAP), and OpenVAS is now distributed as part of Greenbone Community Edition.
Whether you are on the offensive or the defensive side of cybersecurity, there are open-source tools that are free to use and are essential to help you attack or assess and defend systems and networks. Here are 12 free and essential security tools you should already be using!
Nmap
Nmap is a port scanning tool with more capabilities hidden under its scripting engine which you can leverage to detect vulnerabilities and misconfigurations on systems and networks.
Checkout this guide for Nmap tips and techniques.
OpenVAS
Also known as the Open Vulnerability Assessment System (now distributed as part of Greenbone Community Edition). It is a suite of tools that you can use to run tests against clients and discover known vulnerabilities and exploits using its database. You can get it here.
Wireshark
The world’s most famous protocol analyzer. You can use it to troubleshoot network and protocol connections and activity. Available for Windows, Linux, and macOS here.
Nikto
Nikto is a free and open-source scanner that you can use to test web servers for misconfigurations and discover vulnerabilities and attack vectors. With Nikto you can:
- Scan multiple ports on the server
- Find subdomain
- Enumerate users on Apache
- Checks for outdated components
Check this article on how to use Nikto to scan for vulnerabilities and misconfigurations on web servers.
ZAP (formerly OWASP ZAP)
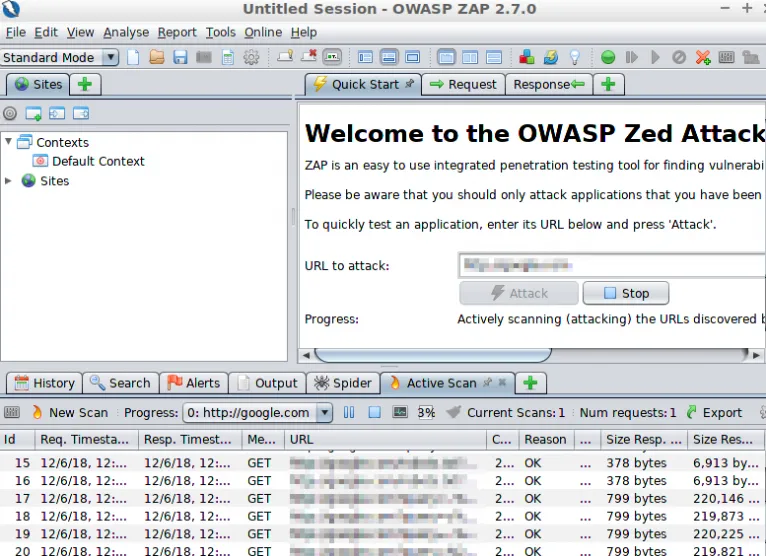
ZAP (Zed Attack Proxy) is an open-source tool, formerly an OWASP (Open Web Application Security Project) project and now an independent open-source project supported by Checkmarx, for penetration testing of your website/web application. It helps you find the security vulnerabilities in your application.
ZAP is an easy-to-use tool. Following are some more reasons for using ZAP:
- Ideal for both beginners and professionals
- Cross-platform – works across all OS (Linux, Mac, Windows)
- Can generate reports of the results
BurpSuite
A very powerful suite of tools. Burp Suite Community Edition is free; Burp Suite Professional is the paid edition and adds the automated vulnerability scanner, among other features. It is a must-have for web application penetration testing. You can leverage its capabilities as an intercepting proxy or crawl content and scan web applications in depth for further analysis, using the repeater and intruder features to find flaws and attack vectors of a web application. It comes preinstalled in Kali Linux, or you can download the free Community Edition here.
Snort
Snort is an open-source network intrusion prevention system, capable of performing real-time traffic analysis and packet logging on IP networks. Snort is a packet sniffer that monitors network traffic in real-time, scrutinizing each packet closely to detect a dangerous payload or suspicious anomalies.
Metasploit
The most advanced framework for penetration testing. You can leverage its capabilities to attack and exploit a system using its tools and payloads. It comes preinstalled in Kali Linux distributions and the is also a paid version you can use.
SQLMAP
This tool is mainly used for detecting and exploiting SQL injection issues in an application and hacking of database servers. It is very powerful and free to use. Get it here.
Social Engineer Toolkit
SET It is an open-source Python-driven tool aimed at penetration testing around Social-Engineering. It has features that let you send emails, java applets, etc containing the attack code.
Aircrack-ng
Are you interested in learning wireless network security? This suite of tools is what you will need. You can use it for WiFi Monitoring, Attacking, and Cracking WEP and WPA-protected networks. Download here.
BeEF – Browser Exploitation Framework
BeEF which stands for Browser Exploitation Framework is a tool that can hook one or more browsers and can use them as a beachhead for launching various direct commands and further attacks against the system from within the browser context.
New tools come out often so make sure you check back here often for more free and essential security tools you can use to assess your systems and networks for weaknesses and vulnerabilities.
Correction, 26 October 2026: this article said the Burp Suite download linked here was the commercial version; it is the free Community Edition, and the paid edition is Burp Suite Professional.